Common ground: six new integrations for network, cloud, security, and platform teams
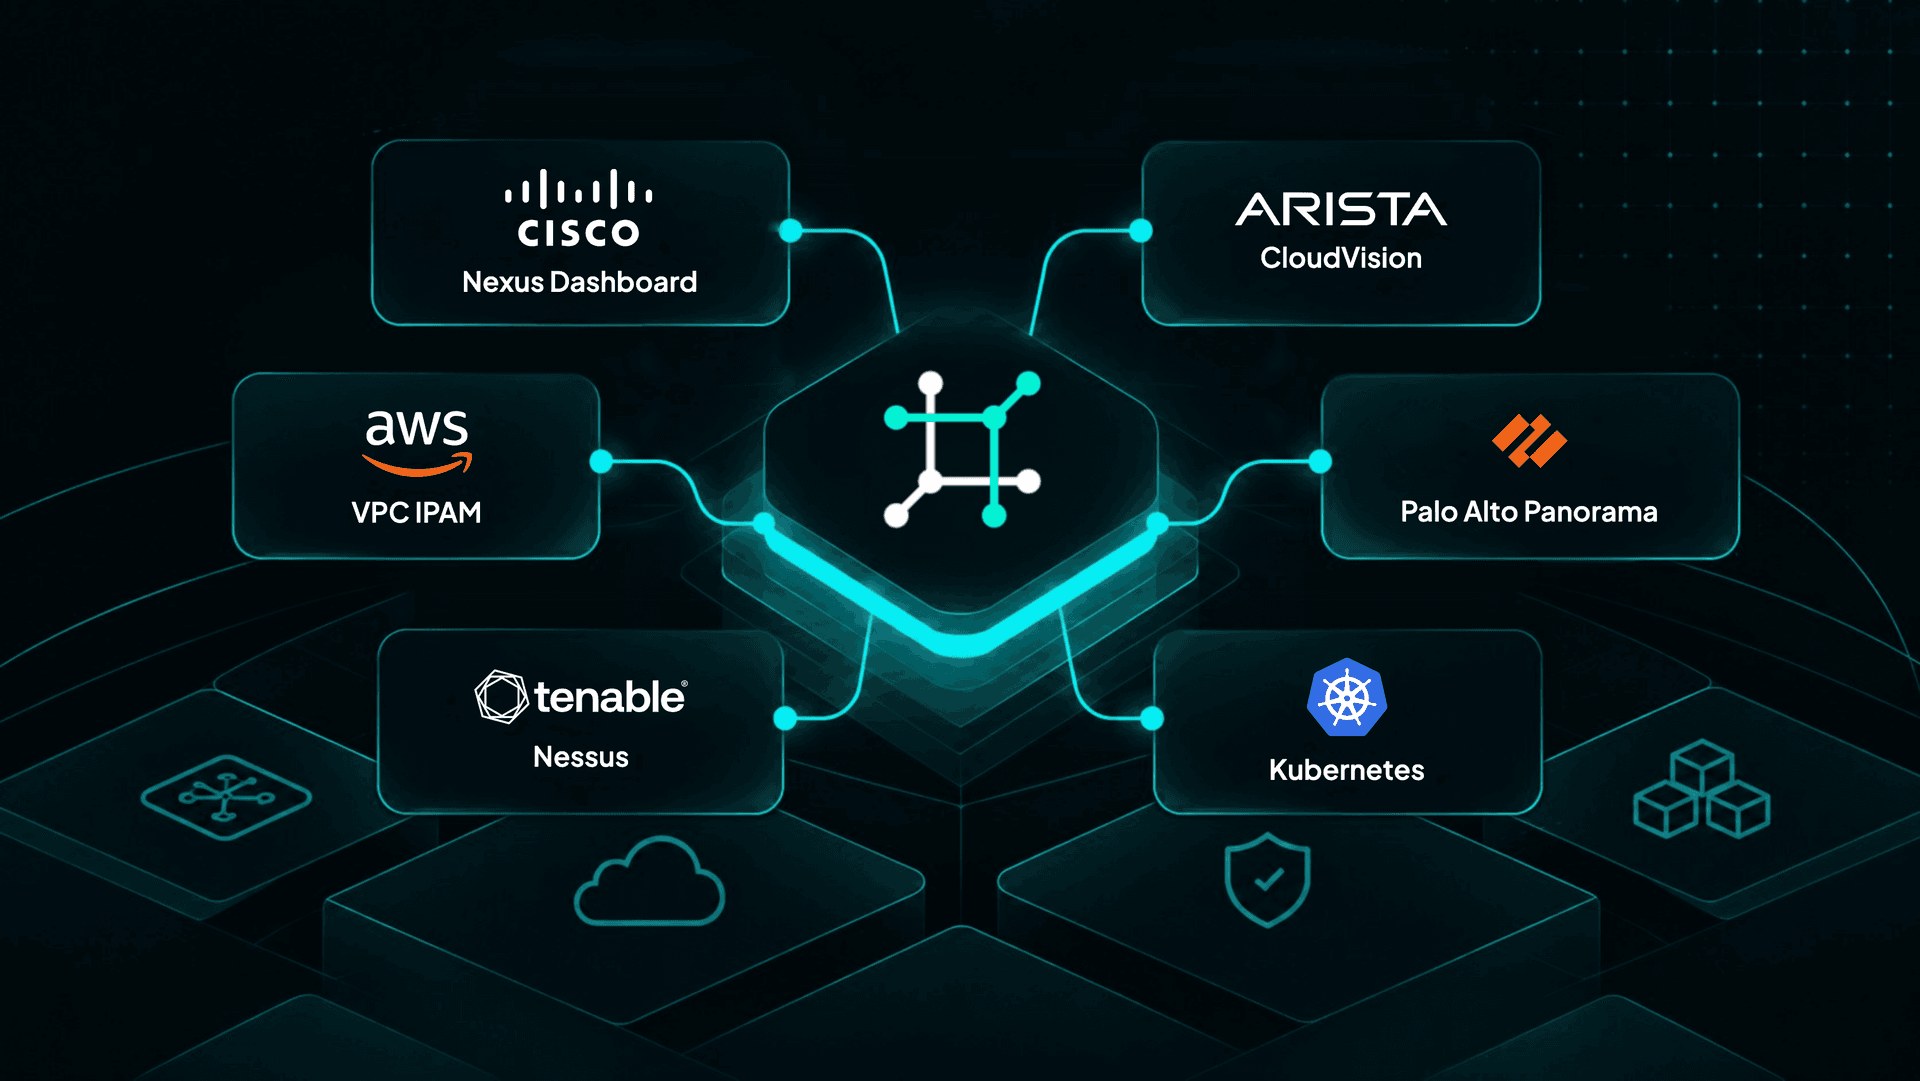
Cisco Nexus Dashboard, Arista CloudVision, and AWS VPC IPAM are generally available, and Palo Alto Panorama, Tenable Nessus, and Kubernetes are in public preview.
The same address space lives in four places. Network teams see it in the fabric controller, cloud teams in AWS, security teams in the latest scan, and platform teams in the cluster. Each view is right for the team that owns it, and none of them sees the others. A range that looks free in one tool may already be taken in another, and a flagged address reaches security with no sign of where it sits.
Today we’re adding six integrations that give those teams common ground in the NetBox Labs platform. Each reads from a tool your teams already run, and that tool keeps its job. What each integration finds comes into one reviewed system of record that people, automation, and agents can work from. Cisco Nexus Dashboard, Arista CloudVision, and AWS VPC IPAM are generally available, and Palo Alto Panorama, Tenable Nessus, and Kubernetes are in public preview.
Every change the integrations find is reviewed first
Configuration and change management failure is the most commonly cited cause of serious network-related outages. In Uptime Institute’s 2026 outage analysis, 41% of respondents who had one named it, more than any other cause. A record your team has reviewed against what is deployed is a better place to plan those changes from.
The integrations read their sources on a schedule and never write back to them. What they find is staged for review in NetBox Assurance, and nothing reaches the record until someone on your team approves it. After the first import, each run stages only what is new or changed. The integrations add and update but never delete, so removing anything from the record stays with your team. NetBox Labs maintains the integrations, so your team has no sync scripts of its own to keep running.

Network teams get fabrics straight from the controllers
Many network teams still copy controller inventory into their system of record by hand, or maintain scripts that break when a vendor API changes. Overlays make it harder because they change faster than anyone can track.
Cisco Nexus Dashboard and Arista CloudVision now bring that inventory straight from the controllers. When a new leaf joins a Nexus fabric, it appears for review on the next sync with its VRFs, VNIs, and the rest of its overlay. CloudVision brings each switch with its layer-3 configuration, and switches carrying CloudVision’s datacenter and type tags arrive sorted by site and role. Both sit alongside the existing Cisco ACI integration. An engineer can find a switch across all three in one place, and audits and automation run on approved data instead of last month’s export.

Cloud teams plan in the same address space
With Gartner expecting 90% of organizations to take a hybrid cloud approach through 2027, many teams now assign addresses across two tools (AWS VPC IPAM for the cloud and the network plan for everything else) and hope they agree.
AWS VPC IPAM now brings its pools and allocations into the record, right beside on-prem prefixes. Each VPC gets its own VRF, so dev, staging, and prod can all run on 10.0.0.0/16 and stay distinct. A central IPAM team can cover many regions and reach into other accounts from one setup. Before anyone assigns a range, cloud and network engineers check it in one place.

Security and platform teams start to see the network
The three preview integrations put firewall, vulnerability, and cluster data in the same record the network and cloud teams already use:
- Palo Alto Panorama brings in Panorama-managed firewalls with their interfaces, IPs, and virtual routers, so a new firewall joins the IP plan on the next sync.
- Tenable Nessus reads scan results from self-hosted Nessus (not Tenable.io or Tenable One) and records each IP address’s highest severity and finding counts, refreshed on every sync. In the preview it matches addresses in the global table only, so addresses held in a VRF, including AWS VPC and cluster ranges, are not matched, and overlapping ranges can collide.
- Kubernetes brings in nodes, pod and service ranges, and LoadBalancer IPs from upstream Kubernetes clusters, with each cluster’s pod and service ranges in their own VRF. OpenShift and other distributions aren’t supported yet.

During the public preview, support is limited to setup and configuration advice, and behavior can change before general availability. If you run Panorama, Nessus, or Kubernetes, your feedback during the preview will help shape where these integrations end up.
Getting started
All six integrations run on NetBox Cloud and NetBox Enterprise with NetBox Assurance. Availability varies by plan, and your account team can confirm what your plan includes. Nexus Dashboard, CloudVision, and AWS VPC IPAM are generally available today. Start with one fabric or AWS account, since the first sync stages everything it finds for review.
For setup, requirements, and object mapping, see the docs for Cisco Nexus Dashboard, Arista CloudVision, AWS VPC IPAM, Palo Alto Panorama, Tenable Nessus, and Kubernetes.
To try Palo Alto Panorama, Tenable Nessus, or Kubernetes in public preview, reach out to your account team. If you’re not a NetBox Labs customer yet, contact us for a walkthrough.